Method for stealing seed phrases via Ledger hardware wallets revealed
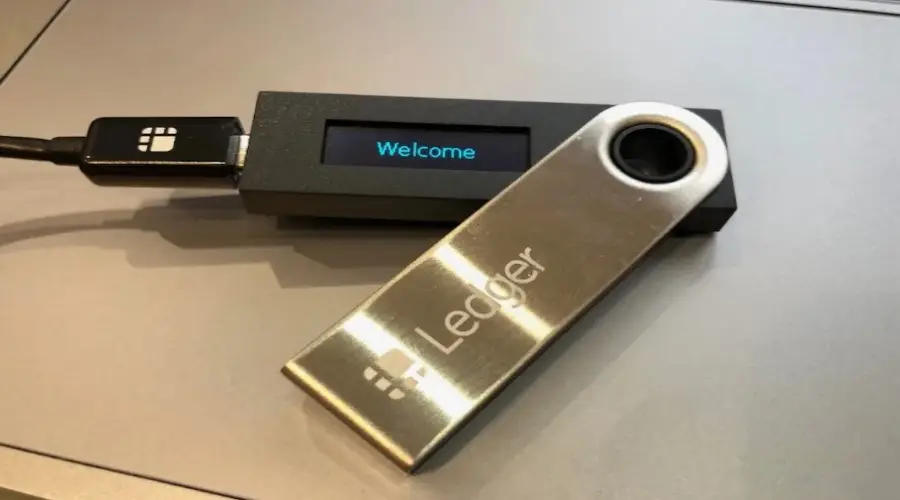
Ledger, the French manufacturer of hardware cryptocurrency wallets, has explained how hidden electronic modules facilitated the theft of cryptocurrency recovery phrases.
A spy module was embedded within the hardware wallet's casing, designed to capture information displayed on the screen. During initial setup, the device would display a 24-word seed phrase to the owner. The spy module’s microcontroller recognized these words and transmitted them via a mobile network using an integrated eSIM.
This unauthorized module operated independently of the wallet's core components. It did not interfere with the Secure Element chip or the operating system, nor did it alter transactions or digital signatures. To steal the secret phrase, attackers simply needed to intercept the information appearing on the screen.
Initially, Ledger acknowledged the presence of the spy module in only one of its devices. The company now confirms that all verified cases of fund loss involve wallets sold through the Asian reseller CryptoBilis; the manufacturer has not observed any thefts involving devices purchased from other vendors. The reseller has halted sales of Ledger wallets—at least for the duration of the investigation.
The manufacturer cannot specify the exact number of victims or the total value of the stolen funds. Independent analysts have estimated the losses at between $70 million and $90 million. Ledger advised customers who purchased devices from CryptoBilis not to set them up, and recommended that those who had already used them transfer their cryptocurrency to a different wallet using a new recovery phrase.
It was previously reported that an investor lost 80 bitcoins—valued at $6.6 million—after transferring the coins to a Ledger hardware wallet purchased from CryptoBilis.